Pre-alpha (v0.2.0). Not for production. Wire formats will change. See the roadmap
WIMSE credentials in. AuthZEN decides. Transaction Token out.
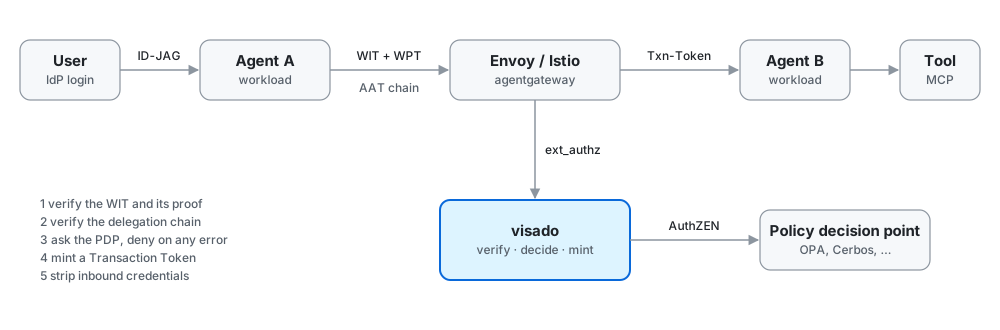
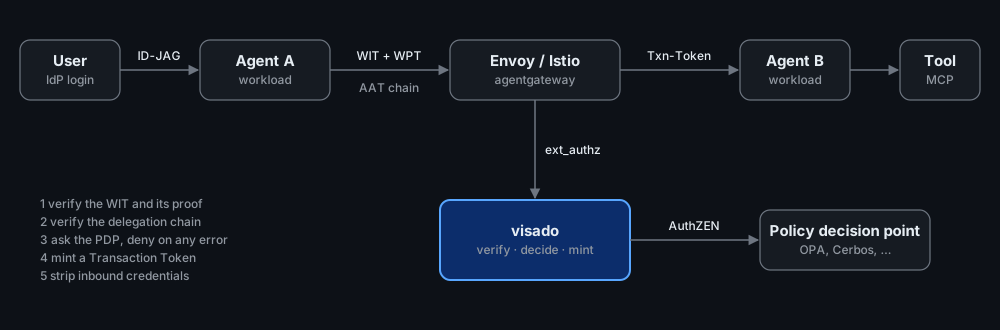
visado is an ext_authz service for Envoy, Istio and agentgateway. For each request it verifies the caller's workload credential or OAuth access token, asks an OpenID AuthZEN 1.0 policy decision point, denies on any error, and sends a signed Transaction Token downstream in place of the caller's credentials. Written in Rust, licensed Apache-2.0.
deploy/lab/demo.sh
- No credentials 401 denied
- Encoded / in the path 400 rejected by Envoy
- agent-a reads tickets for bob 200 allowed
- agent-b forwards bob's transaction to the admin API 403 denied by the PDP
- agent-b forwards bob's transaction to tickets 200 allowed
- A workload outside internal_callers forwards it 403 denied
- User token without roles.write on the admin API 403 denied by the PDP
- carol, with roles.write, through agent-a 200 allowed
- AAT: agent-b reads the file agent-a delegated 200 allowed
- AAT: agent-b reads another file 403 denied by the chain
- AAT: agent-b calls a tool agent-a kept 403 denied by the chain
- AAT: agent-z presents agent-b's chain 403 denied by the chain
Envoy, visado, OPA with the AuthZEN plugin and an echo upstream. CI runs all of them.
Quick start
The lab puts visado behind Envoy with OPA as the policy decision point and runs the scenarios above. You need Docker with Compose.
git clone https://github.com/kanywst/visadocd visado/deploy/labdocker compose up -d --build./demo.sh
Each decision also shows up as a visado.authorize span in Jaeger at
http://127.0.0.1:16686. The demo keys are public; do not reuse them.
Lab guide
How a request goes through
The proxy sends each request to visado over ext_authz. visado runs the steps below in order and stops at the first failure. Only an allowed request reaches the upstream, carrying a Transaction Token instead of the caller's credentials.
 Envoy
 Istio
 PDP in the lab
 Open Policy Agent
-
Sanitize
Deny authorities outside allowed_authorities and paths an upstream could resolve differently. Accept an inbound Txn-Token only from a configured internal caller.
Since v0.1.0
-
Authenticate
Verify a WIMSE Workload Identity Token with a WPT or an HTTP message signature, an X.509-SVID over mTLS, a JWT-SVID, or an OAuth access token, bearer or DPoP-bound. Keys come from configuration, never from URLs inside a token.
WIT with WPT since v0.1.0; HTTP signatures, mTLS, JWT-SVID and DPoP since v0.3.0. Each runs behind Envoy in the lab.
-
Verify the delegation chain
Verify an AAT chain (AAT-Chain and AAT-PoP), an asor Agent Delegation Chain, or the RFC 8693 act claim of an access token. The holder or current actor must be the caller that proved a key. An AAT call is denied unless the chain permits this tool with these arguments.
AAT since v0.2.0; asor and RFC 8693 act since v0.3.0.
-
Authorize
Send an AuthZEN 1.0 evaluation request: the agent is the subject, the user is context.principal. Timeouts, transport errors, non-200 answers and non-boolean decisions all deny.
Since v0.1.0.
-
Mint
Sign a Transaction Token (typ txntoken+jwt), add it as the Txn-Token header and remove the inbound Authorization header before the request goes upstream.
Since v0.1.0. JWKS at /.well-known/jwks.json.
-
Record
Write a JSON audit event and a visado.authorize OpenTelemetry span for every decision, with a stable reason code on denials.
Audit events since v0.1.0, OpenTelemetry spans since v0.2.0, the chain view since v0.3.0.
Full pipeline and plugin interfaces: design.
Standards, pinned
visado has no token format of its own. It implements published specifications at a fixed revision and records every place it departs from them.
| Specification | Revision | Status |
|---|---|---|
| OAuth Transaction Tokens | draft-ietf-oauth-transaction-tokens-11 |
Implemented Mint, verify, replace, request parsing. 5 valid and 22 negative conformance vectors. |
| OpenID AuthZEN Authorization API | 1.0 Final |
Implemented Single evaluation and metadata discovery. Batch and search are not used. |
| WIMSE workload credentials (WIT, WPT) | pinned in wimsey |
Implemented WIT with WPT; HTTP signatures (draft-ietf-wimse-http-signature-08) and mTLS since v0.3.0. |
| JWT access tokens | RFC 9068 |
Implemented Accepted alone, bound to a WPT or HTTP signature, or DPoP-bound (RFC 9449, since v0.3.0). |
| Envoy external authorization | ext_authz v3 |
Implemented gRPC service. Runs behind Envoy in the lab. |
| Attenuating Agent Tokens (AAT) | draft-niyikiza-oauth-attenuating-agent-tokens-02 |
Implemented §8 verification, 229/229 published vectors, enforced by the gate. Since v0.2.0. |
| Agent delegation chain (asor) | draft-asor-wimse-agent-delegation-chain-03 |
Implemented §6 verification with DPoP, 36/36 published vectors, enforced by the gate. Since v0.3.0. |
| Token Exchange actor claim (act) | RFC 8693 §4.1 |
Implemented The current actor is bound to the caller; prior actors are recorded, not used for decisions. Since v0.3.0. |
| Identity Assertion Authorization Grant (ID-JAG) | draft-ietf-oauth-identity-assertion-authz-grant-06 |
Planned |
| WIMSE AI agent identity (AIMS) | draft-ietf-wimse-aims-01 |
Reference The composition visado follows. Not implemented as such yet. |
Divergences and choices, section by section: spec map.
The Transaction Token vectors in conformance/
can test other implementations.
What it is, and what it is not
visado is the check at the enforcement point. It authenticates the caller, verifies the chain of delegation behind the request, gets a decision and hands the next hop a token that says who is acting for whom.
It is not a policy decision point, not an identity provider and not a gateway. It has no policy language: decisions come from an AuthZEN 1.0 PDP. The lab uses OPA with the AuthZEN plugin; a Cedar or OpenFGA deployment reaches visado through an AuthZEN endpoint in front of it.
SPIRE issues the workload identities visado verifies. Envoy, Istio and agentgateway route the traffic and call visado through ext_authz.
| Need | Use |
|---|---|
| Issuing workload identities | SPIRE, any WIMSE issuer |
| User login, ID-JAG issuance | Dex, Keycloak, Okta, Entra, Casdoor |
| OAuth authorization server, agent IdP | Keycloak, zeroid, ToolHive |
| Policy evaluation | Any AuthZEN 1.0 PDP |
| Routing, MCP multiplexing, LLM proxying | agentgateway, Envoy, ContextForge |
| Vaulting SaaS tokens, consent UI | Zalando Agentic Identity Broker, Infisical Agent Vault |
Works with
- Calls visado over ext_authz
-
Envoy
Istio
- Envoy runs in the lab. Istio and agentgateway use the same ext_authz v3 API and are not in the lab yet.
- Issues the identities visado verifies
-
 SPIFFE
 SPIRE
- WIT verification since v0.1.0; X.509-SVID and JWT-SVID verification since v0.3.0. SPIRE issues the WIT-SVIDs in the lab.
- Decides, behind an AuthZEN 1.0 API
-
Open Policy Agent
 Cedar
 OpenFGA
- OPA with the AuthZEN plugin runs in the lab. Cedar and OpenFGA need an AuthZEN endpoint in front of them and are untested.
Scope in full, with neighbouring projects: scope.
Security
Fails closed
- Any verification error, PDP error or non-boolean decision denies the request.
- Inbound credentials are removed before the request goes upstream; a Txn-Token is forwarded only from configured internal callers.
- Ambiguous paths and unknown authorities are denied before authentication.
- Both listeners bind to loopback by default.
Threat model, including the incidents visado does not stop.
Signed releases
Every release asset, the SPDX SBOM and SHA256SUMS are signed keylessly with
cosign, and the binaries carry SLSA build provenance. The release notes show the
cosign verify-blob command for that release.
Reporting a vulnerability
Use GitHub private vulnerability reporting. Do not open a public issue or pull request.
Where it stands
- 0 Foundation Met
- 1 Transaction Tokens Met
- 2 ext_authz and caller authentication Partly met
- 3 Delegation chains Partly met
- 4 AuthZEN Partly met
- 5 Lab, visibility and demos Started
- 6 Interop and launch Not started
Help wanted
- Running the AuthZEN profile against a second PDP besides OPA
- Dex, Keycloak and agentgateway in the lab
- Transaction Token interop with other implementations, using the conformance vectors
Get involved
- GitHub issues Bugs, questions, spec discussions.
-
Contributing
Every commit needs a DCO sign-off (
git commit -s). - Code of Conduct Expected behaviour, and how to report a violation.
© 2026 The visado Authors. Licensed under Apache-2.0.
Third-party logos are trademarks of their respective owners and are used to show compatibility; their use does not imply endorsement.